neonotu GmbH
Booth number: 50123-20
www.neonotu.com
About us
neonotu is a Munich-based cybersecurity company that helps organizations of every size find, fix and stay ahead of security risks. Founded in 2016, neonotu combines hands-on security services, from penetration testing and red teaming to incident response, digital forensics and virtual CISO support, with its own cybersecurity suite, developed in Europe and operated in data centers in Germany and the EU.
At CES 2027, neonotu presents three products:
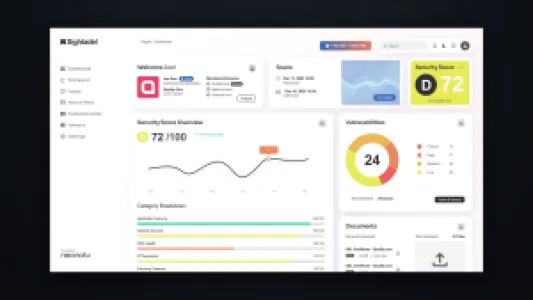
Sightadel brings information security and compliance into one system, covering ISO 27001, NIS2, GDPR, DORA and more, so teams stay audit-ready all year.
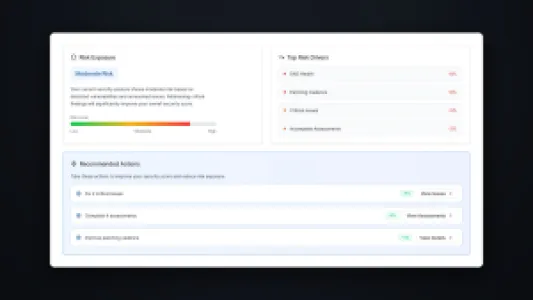
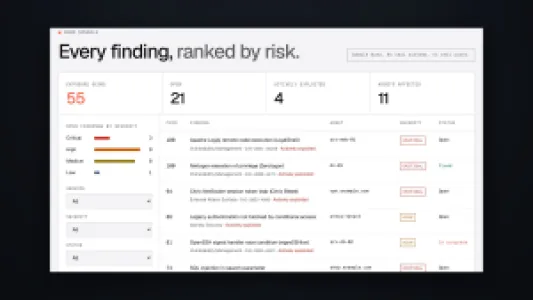
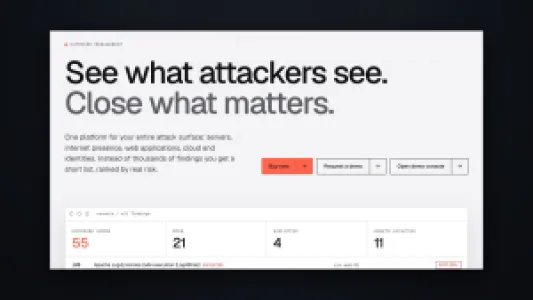
veyrisk gives companies a continuous view of their exposure: vulnerabilities, external attack surface, web applications, cloud and identities, ranked by real risk.
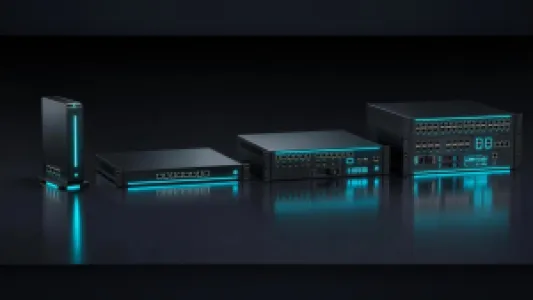
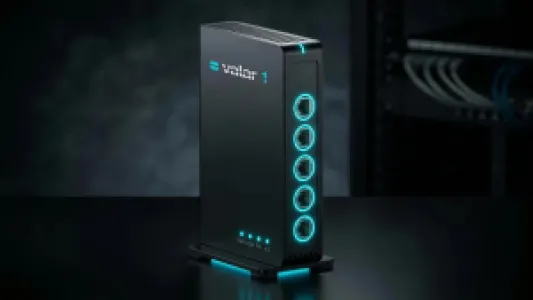
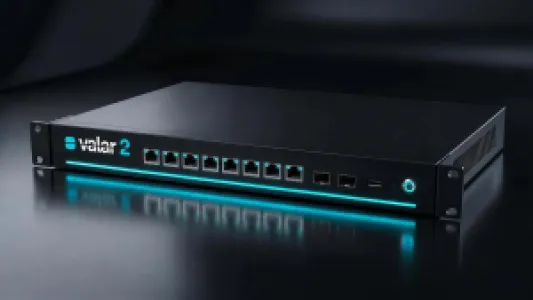
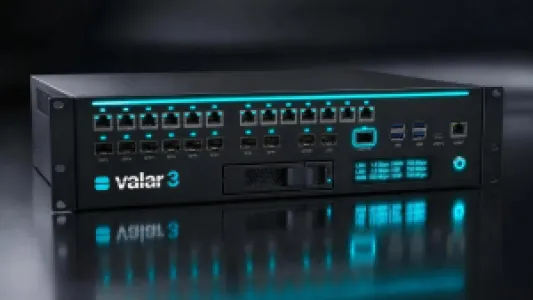
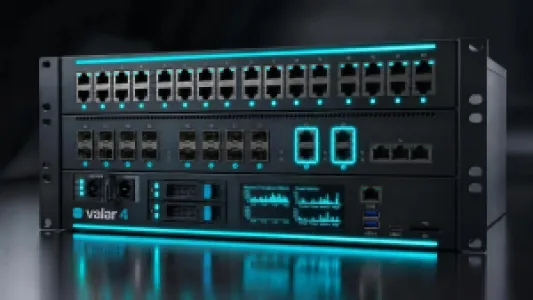
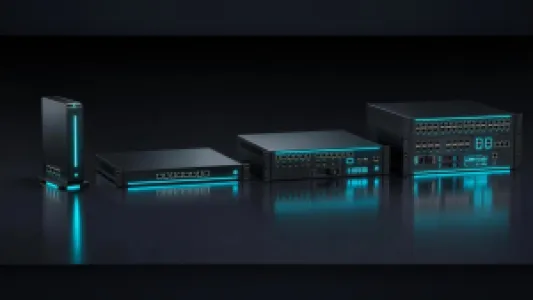
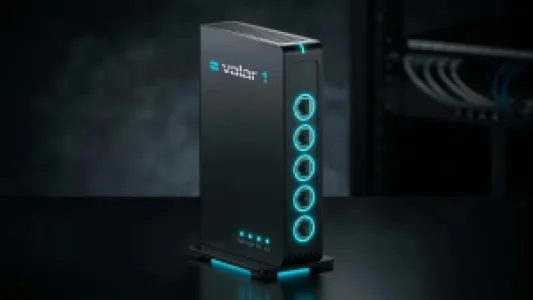
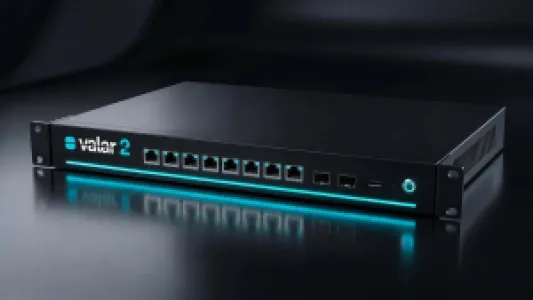
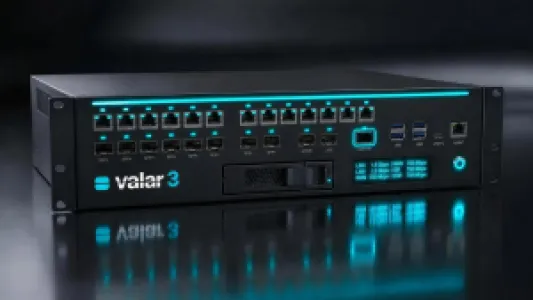
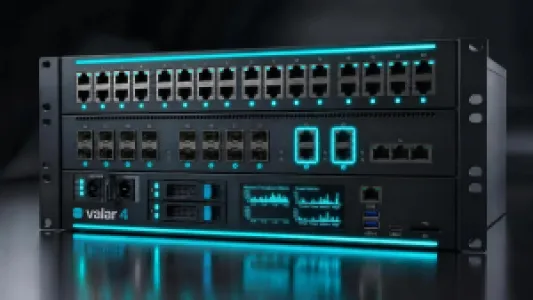
Valar is a line of hardware firewalls made in Europe. Four models protect the network perimeter and internal zones, from a single medical practice to enterprises with thousands of seats, with AI-based detection built into every model.
neonotu is ISO 27001 and ISO 9001 certified and employs 25 people in Munich, Tarifa (Spain) and Tallinn (Estonia).
Address
Edelsbergstraße 8
80686 München
Germany
E-mail: mail@neonotu.com
Phone: +49 89 200079750
Internet: www.neonotu.com
Contact person:
Products & Services
Valar: Hardware Firewalls Made in Europe
Four models, one management logic. Valar secures the network perimeter and internal zones for anyone from a single medical practice to a critical-infrastructure operator. Every model includes AI-based detection.
Sightadel
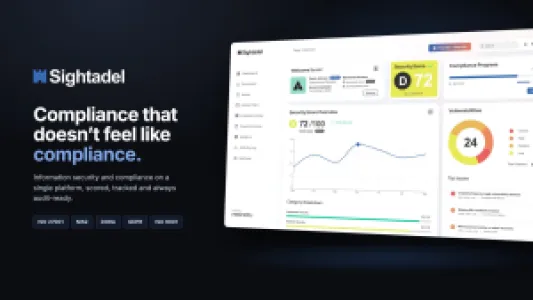
Sightadel: Compliance That Doesn't Feel Like Compliance
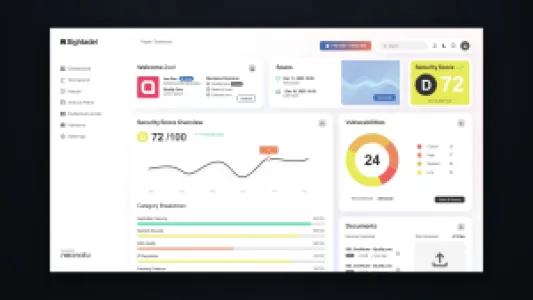
Sightadel brings an organization's entire security and compliance posture onto a single platform. Requirements from ISO 27001, NIS2, DORA, GDPR and ISO 9001 are managed in one place. A live security score, action plans and an evidence locker keep teams audit-ready all year. It is part of the neonotu cybersecurity suite, developed in Europe and hosted in data centers in Germany and the EU.
veyrisk: Exposure Management for Growing Companies
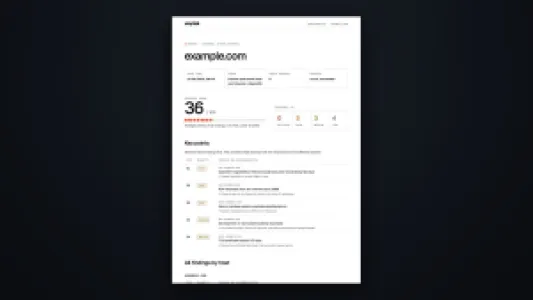
veyrisk shows companies what attackers see and what to fix first. The platform scans your entire attack surface continuously: servers and infrastructure, your external internet presence, web applications and APIs, cloud accounts and identities such as Microsoft 365 and Entra ID. Instead of thousands of raw findings, you get a short list ranked by real risk. Each finding is weighed by severity, known exploitation and how important the affected system is. An exposure score from 0 to 100 tracks progress over time.
Clear PDF reports give management, auditors and IT partners the evidence they need, for example for ISO 27001 and NIS2. External scans run only on domains whose ownership has been verified. Cloud checks need read-only access and nothing more.
veyrisk is built for small and mid-sized businesses without a dedicated security team. It is developed and operated by neonotu in Germany, is GDPR-compliant and comes in three plans that scale with your environment.